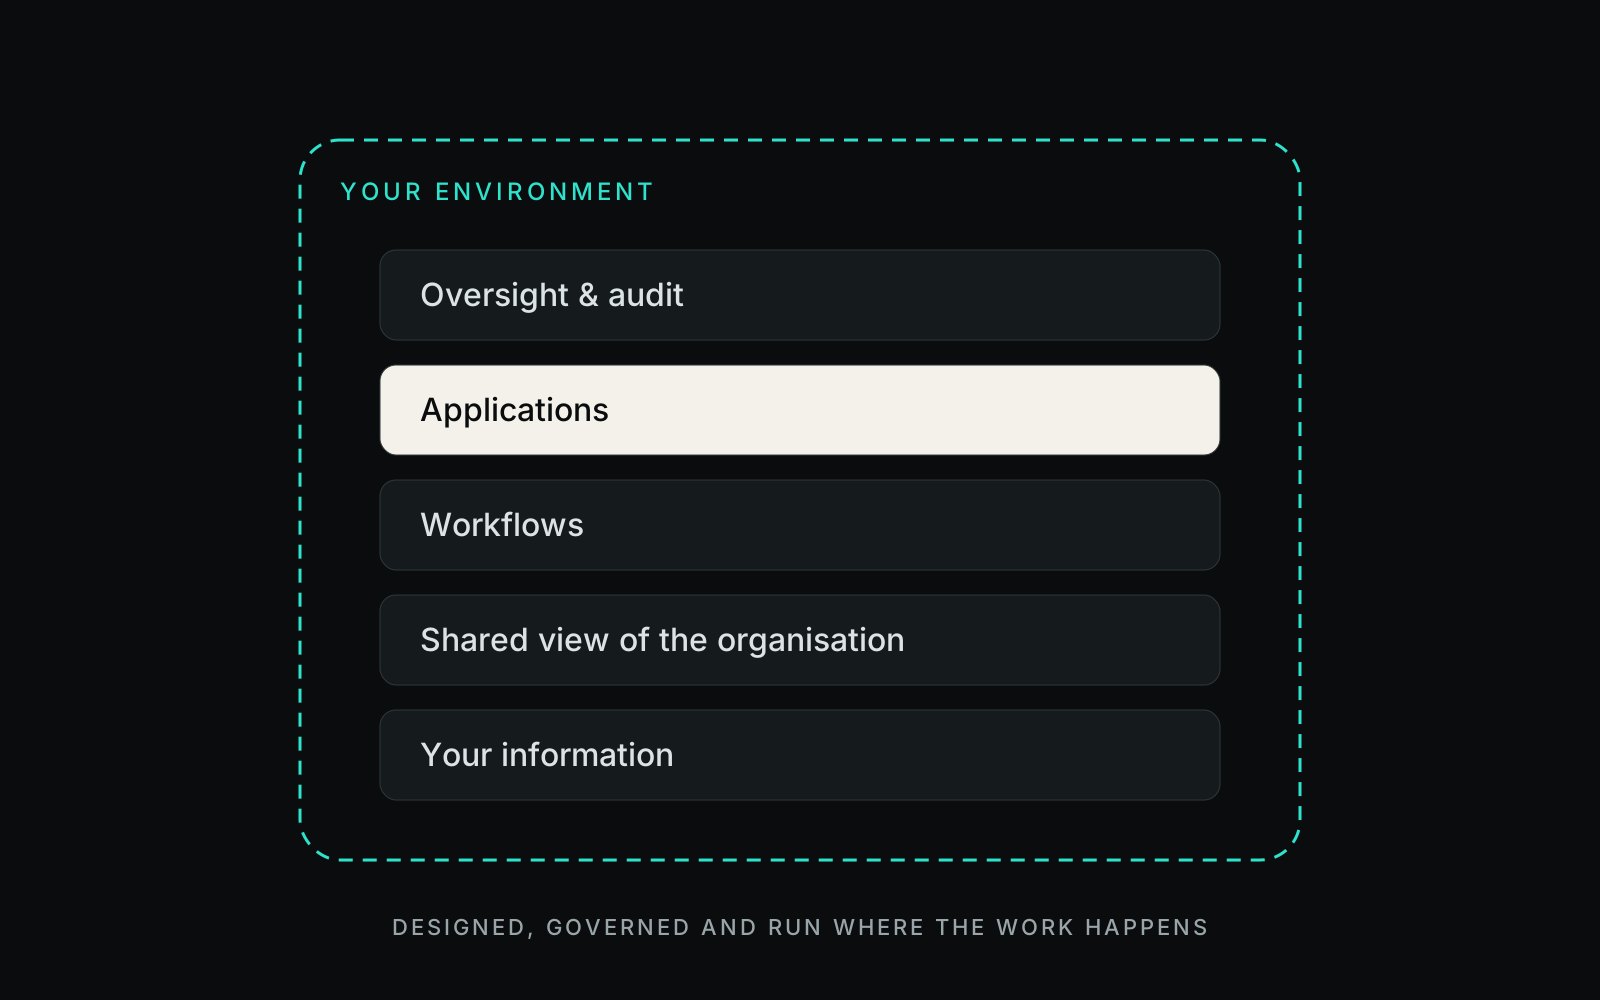
When an application supports critical decisions, the important questions are not only technical. They are about who designs it, who governs it and who is accountable when it matters.
Security is often discussed as a feature: encryption, access controls, certifications. These matter. But for governments and regulated organisations, a more fundamental question sits underneath: where is the system designed, where does it run, and who answers for it?
Control is designed in, not added on
An application that will handle sensitive information should be shaped around your environment from the first day: your systems, your security requirements and the way your people actually work. Retrofitting controls onto a generic product rarely achieves the same level of confidence.
Accountability needs to be close
When something changes, such as a new regulation, a new risk or a new priority from leadership, the team responsible for the system needs to understand the context and respond quickly. A team on the ground, working alongside your people, can do that in a way a distant supplier cannot.
Your information stays under your control. Your people stay involved.
What to look for
- Applications that can run on your own servers, in a private or national cloud, or fully offline.
- Permissions, audit trails and approval steps built in from the start.
- Freedom to choose and change the underlying technology, without being tied to one vendor.
- A delivery team that is local, accountable and measured against your outcome.